
GDPR: What Every Small Business Owner Should Be Checking Right Now
Key takeaways from our September Online Business Mastermind Hour with Lucy Wheeler
GDPR. Privacy policies. Cookies. Data processing agreements. AI tools.
For many small business owners, the legal side of running a business can quickly move into the “I know I need to deal with it, but I’m not quite sure where to start” pile.
That was exactly what we wanted to tackle at our September Online Business Mastermind Hour.
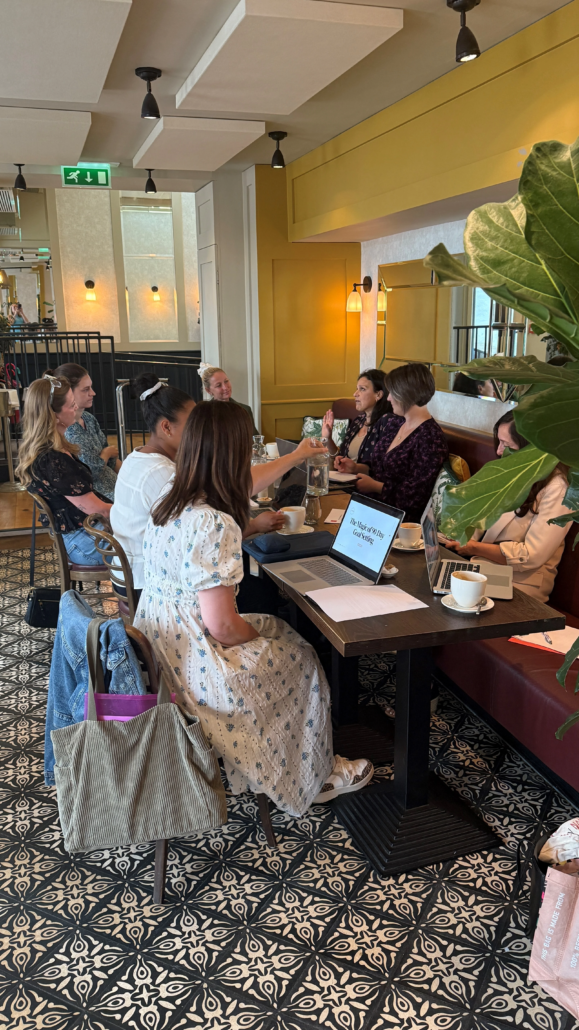
We were joined by qualified solicitor and founder of Lucy Legal, Lucy Wheeler, for a practical session designed to help women founders understand what GDPR actually means for a small business, what has changed in 2026, and some of the areas we should all be checking.
Lucy’s aim was to make the legal side of business feel less daunting and give founders more confidence in understanding their responsibilities.
And judging by the number of questions that followed, there was plenty for us all to think about!
Here are some of the biggest takeaways from the session.

GDPR Is About More Than Having a Privacy Policy on Your Website
One of the most important messages from Lucy was that GDPR compliance isn’t simply a case of adding a privacy policy to the footer of your website and forgetting about it.
You need to think about what actually happens to personal information throughout your business.
That includes:
How do you collect it? Where is it stored? Who can access it? Why are you collecting it? How long do you need it? What happens when a member of your team leaves?
Lucy encouraged everyone to look at GDPR as an ongoing business process rather than a document.
Your privacy notice communicates what you do with people’s information, but your everyday processes need to reflect what that notice says.
Do You Need a Data Processing Agreement?
This created a really interesting discussion.
If you work inside another business and process personal data on its behalf, you may need a Data Processing Agreement (DPA).
During the session, we looked at the example of a digital marketer who can access clients’ websites, email databases and customer information.
Lucy explained why business owners need to understand the distinction between simply carrying out an administrative function and actually processing or analysing personal data on behalf of another organisation.
It’s particularly relevant to VAs, marketers, consultants, freelancers and other outsourced specialists who regularly work inside their clients’ systems.
The takeaway?
Don’t assume your normal client contract covers everything.
Look at exactly what access you have and what you’re doing with the information.
There’s an Important New Data Protection Complaints Requirement
This was probably one of the biggest “I need to check that!” moments from the session.
Changes introduced under the Data (Use and Access) Act 2025 came fully into force on 19 June 2026. One of the practical changes for businesses is a new requirement around data protection complaints.
Organisations handling personal information now need to provide people with a clear way to make a data protection complaint, acknowledge complaints within 30 days, investigate them appropriately and communicate the outcome.
That means this is a good time to review your privacy information and complaints process.
Can someone easily see how to raise a complaint about the way you’re handling their data?
Do you know what would happen internally if they did?
It doesn’t necessarily require an elaborate new system, but it does need a clear process.
Check Whether You Need to Pay the ICO Data Protection Fee
Another useful discussion was around the Information Commissioner’s Office (ICO) and the annual data protection fee.
Not every business has to pay it, so don’t guess.
The ICO has a self-assessment tool that tells organisations whether they need to pay and, if so, which fee applies.
Check whether you need to pay the ICO data protection fee
It’s a small piece of business admin that can be very easy to overlook.
Email Marketing: Consent, Opt-Ins and Existing Customers
This prompted one of the liveliest conversations of the hour.
Can you email previous customers if they never explicitly ticked a marketing consent box?
Lucy discussed the circumstances in which businesses may be able to contact existing customers about similar products or services.
This is an area where it’s important to be precise. Current ICO guidance says the soft opt-in can allow marketing to previous customers without explicit consent, but only when its specific conditions are met—including having given the person a clear opportunity to opt out when their details were originally collected and in every subsequent marketing message.
For new email sign-ups, consent shouldn’t be assumed with a pre-ticked box.
A useful action from the session is therefore to review how people currently enter your database, what you’ve told them at that point and whether your email marketing process gives them the appropriate choices.

AI Has Added a Whole New Layer to Data Privacy
This was perhaps the most thought-provoking part of the session.
We’re increasingly using AI tools without necessarily stopping to think about the data we’re giving them access to.
AI note takers, meeting transcription, chatbots, automated DMs, AI agents accessing inboxes and platforms where client information is uploaded all raise questions around privacy and transparency.
Lucy encouraged everyone to ask:
What data is this AI tool accessing – and have I considered whether I have the right permissions and processes in place?
One particularly useful example involved AI note takers.
Just because your note taker automatically joins every meeting doesn’t necessarily mean it should.
If you’re hosting a meeting, consider how attendees are informed about recording or transcription and what happens to that information afterwards. If you’re attending somebody else’s meeting, bringing your own automated note taker into the room can create an entirely different data-handling relationship.
Sometimes the best question isn’t “Can this tool record everything?”
It’s:
“Do I actually need it to?”
That principle applies to AI more widely too.
Your Privacy Information Needs to Keep Up with Your Technology
Businesses change quickly.
You introduce a new CRM.
Start using an automation platform.
Add an AI tool.
Change your email software.
Bring in a freelancer.
But when did you last check whether your privacy information reflects how your business actually operates today?
Lucy suggested reviewing the platforms and tools that handle personal information and making sure your privacy information remains accurate.
She also discussed considering a separate AI policy where appropriate, particularly as the way businesses use AI is likely to evolve much faster than many other systems.
A Simple GDPR Check for Your Business
Rather than GDPR feeling like one enormous job, break it down into practical actions. Use this checklist as a starting point:
- Review your Privacy Notice – does it accurately reflect how you currently collect, use, store and share personal data?
- Check your data protection complaints process – is it clear how someone can raise a complaint and how you will handle it?
- Check whether you need to pay the ICO data protection fee – use the ICO self-assessment tool if you’re unsure.
- Review who has access to personal data – including employees, freelancers, VAs and external suppliers.
- Check whether you need Data Processing Agreements (DPAs) – particularly where you or another business processes personal data on someone else’s behalf.
- Review your email marketing processes – check how people join your list, what they’ve been told and how they can opt out.
- Audit your AI tools – what customer or client information can they access, process or store?
- Check recording and transcription tools – including AI meeting note-takers and how attendees are informed.
- Review your automations and software – know which platforms are handling personal information and why.
- Check how and where data is stored – including CRMs, email platforms, cloud storage, laptops and handwritten notes.
- Remove unnecessary access – especially when employees, freelancers or suppliers stop working with you.
- Only collect the information you actually need – don’t hold personal data simply because you can.
- Review how long you keep personal information – and have a process for securely deleting information you no longer need.
You don’t have to tackle everything at once. Pick two or three things to check this week and work through the rest.
The important thing is knowing what personal data your business holds, why you have it, where it goes and how you’re protecting it.
The Value of Asking GDPR Questions
One of the things we loved most about this Online Business Mastermind Hour was the conversation it created.
Members were able to bring real examples from their businesses and ask the questions they might otherwise have continued wondering about.
Can I email these customers?
Do I need a DPA?
What about my AI note taker?
Should this tool be mentioned in my privacy policy?
Do I need to pay the ICO fee?
And that’s exactly why we run these sessions.
Sometimes you don’t need another generic business article or another hour spent Googling.
You need the opportunity to ask an expert, “But what does this actually mean for my business?”
More Than Networking: How COCO Supports Women In Business
At COCO Women Founders, we believe women in business need more than somewhere to swap business cards.
Running a business can be isolating, and you shouldn’t have to work everything out alone.
Our community brings together ambitious women founders and women in business to build meaningful relationships, but also to learn, share challenges, ask questions, gain fresh perspectives and take practical action.
Alongside our in-person Business Networking & Mastermind events in Amersham, Beaconsfield, Marlow and Thame, we run Online Business Mastermind Hours, expert workshops, 90-day goal-setting sessions and social events.
It’s about having a community around you that understands the realities of running a business – while giving you the support, learning and accountability to keep moving forward.
Together We Grow. 💗
The Speaker: Lucy Wheeler
Lucy Legal
Lucy Wheeler is a qualified UK solicitor and founder of Lucy Legal, which she established in 2019. Since 2020, she has focused on supporting entrepreneurs, combining her legal expertise with first-hand experience of running a business herself.
Her approach is about making the legal side of business feel less intimidating and helping entrepreneurs understand not simply what the law says, but what they need to think about in the context of running their own businesses.
As Lucy explained during the session, understanding the legal side of your business is ultimately about understanding risk: What could go wrong? What do I need to have in place? And what steps can I take to protect and strengthen my business?
This article summarises general information discussed during the COCO session and is not legal advice. Businesses should take advice relevant to their own circumstances where required.
Exclusive COCO Member Offer
Following our GDPR Mastermind Hour, Lucy Wheeler is offering COCO members an exclusive discount on Lucy Legal templates, covering key legal documents to help protect your business.
COCO members can get in touch with Vicky for the discount code.


